Security guide · 8 min read
Safe HTML-to-PDF Conversion: Scripts, Remote Resources and Privacy
Learn why active HTML, remote resources, redirects, and private-network access need a strict security boundary during PDF conversion.
Published and technically reviewed by the PDFStack Team · October 14, 2026
HTML is active input
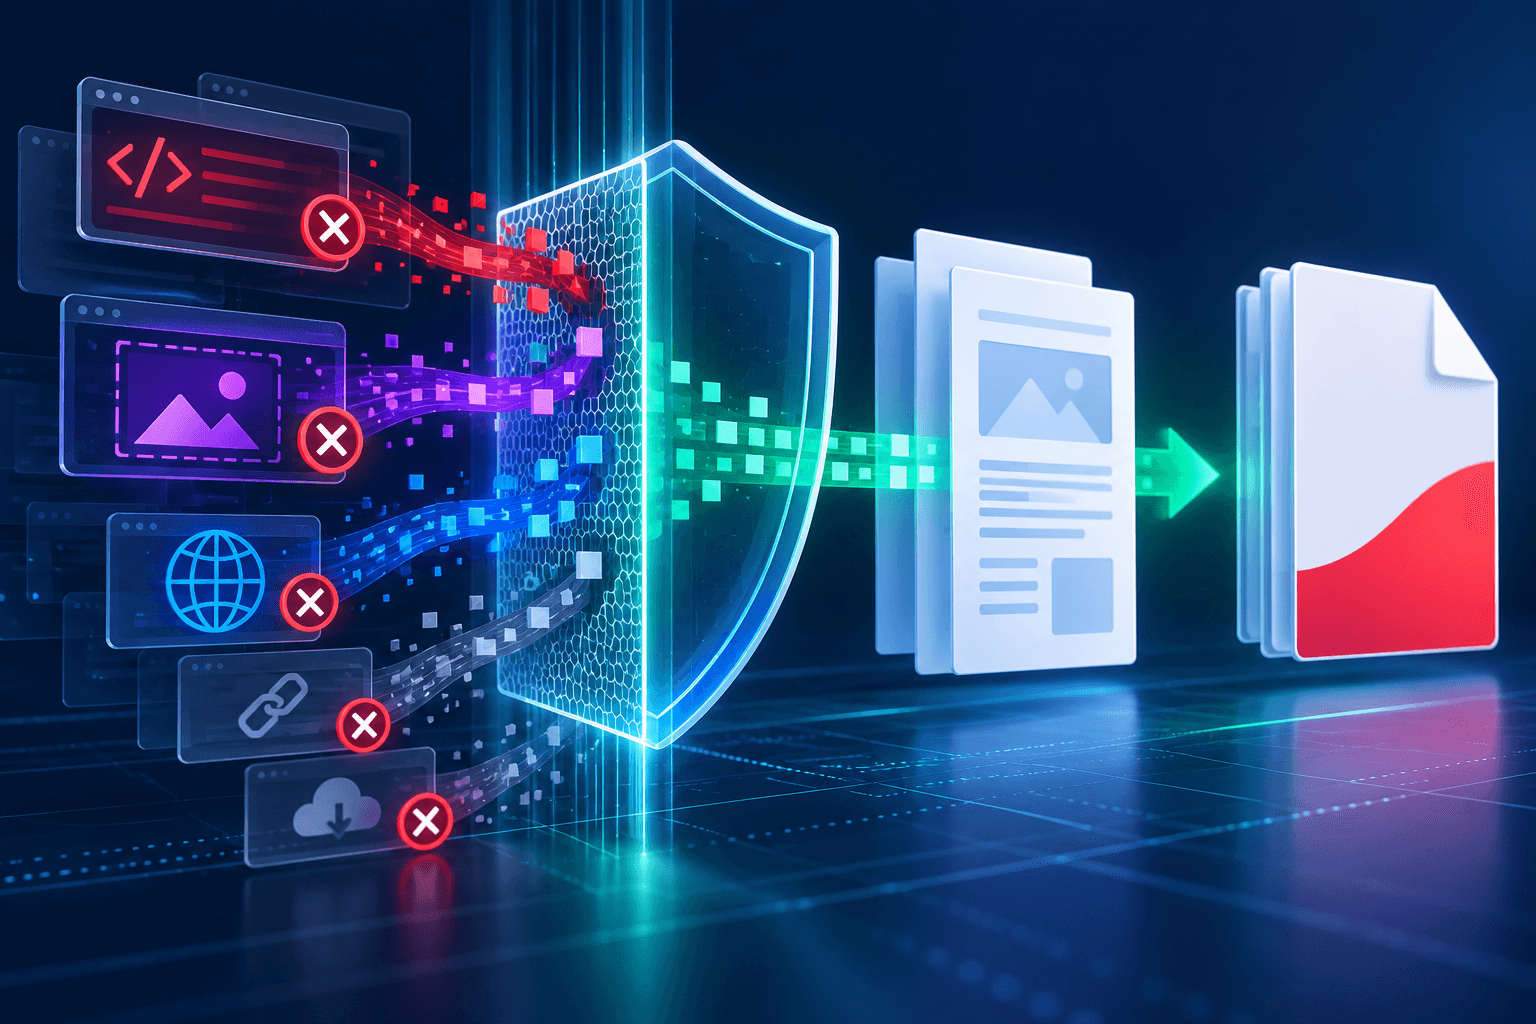
An HTML file can contain scripts, frames, form actions, remote images, tracking pixels, event handlers, and links to local or private resources. Treating it as harmless formatted text creates avoidable security and privacy risk.
A constrained local workflow should parse the document without executing scripts. It should remove active elements, reject unsafe URI schemes, and avoid unrequested network access.
URL capture has a larger attack surface
A service that accepts a webpage URL becomes a network client. Attackers may target loopback services, cloud metadata endpoints, private IP ranges, oversized downloads, redirect chains, or DNS records that change after validation.
Safe URL capture needs outbound network policy, DNS-rebinding resistance, redirect revalidation, response and time limits, content-type enforcement, and a sandboxed browser. Disabling URL capture is the correct decision when those controls are absent.
- ✓Block private and link-local networks.
- ✓Revalidate every redirect.
- ✓Limit response bytes and render time.
- ✓Isolate the browser and temporary files.
- ✓Do not retain documents longer than necessary.
Remote resources can reveal user activity
Loading an image, stylesheet, or font can disclose IP address, timing, referrer information, and document-specific tokens to another server. Authenticated resource URLs can also expose confidential material if logs or generated files are mishandled.
Self-contained HTML is easier to reason about. Embed only resources that are safe and licensed, remove secrets from query strings, and inspect the sanitized source summary before conversion.
Make limitations visible
Security controls change rendering behavior. If scripts are removed or remote resources are not fetched, the product should explain that outcome rather than imply a complete browser screenshot.
The result page should preserve the source, show output size and page count, and let the user preview before sharing. Security and usability are strongest when users can verify the exact artifact they will distribute.
Frequently asked questions
Is it safe to execute uploaded HTML?
Uploaded HTML should be treated as untrusted. A local text-first workflow can parse and sanitize it without executing active content.
Why is URL conversion disabled?
URL capture requires hardened network and browser isolation controls. Disabling it avoids exposing internal services or fetching unsafe content.