

Access controls · 9 min read
File Transfer Expiry, Passwords and Download Limits Explained
Understand what transfer-link expiry, password protection, revocation and download allowances control—and what they cannot guarantee.
Published and reviewed by the PDFStack Team ·
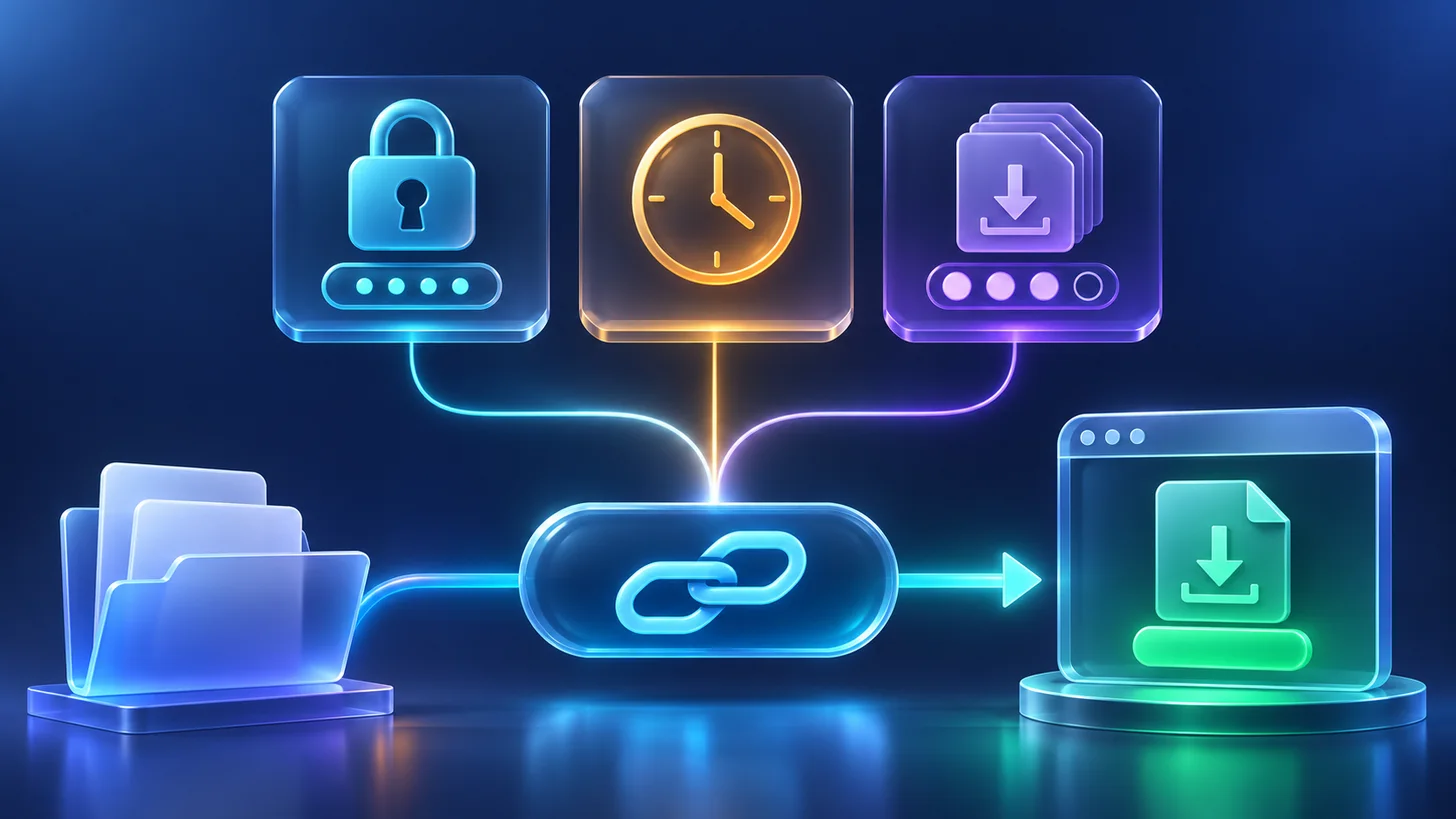
Each control answers a different question
An expiring transfer link defines when the service should stop granting access. A password adds a secret the recipient must provide. A download allowance controls how many service-authorized downloads remain. Revocation lets the sender close access before the planned expiry.
These controls are complementary rather than interchangeable. A long-lived link with a weak password is not equivalent to a short-lived link shared with a verified recipient, and a one-download setting does not erase a file already saved to another device.
Choose an expiry window deliberately
Nexynto Transfer currently presents 1, 3, 7, and 14-day expiry choices. Select the shortest window that still accommodates the recipient’s schedule, time zone, and approval process. Avoid choosing a longer duration merely to prevent a follow-up message.
Expiry is enforced by the service for future access. It does not recall copies downloaded before the deadline. If a deadline changes, verify whether a new transfer is clearer than extending access through another channel.
- Use one day for prompt, coordinated delivery.
- Allow more time when multiple reviewers are expected.
- State the expiry in the delivery message.
- Revoke early when the handoff is complete or cancelled.
Use passwords as an additional access check
Password protection helps when a link is forwarded or exposed, provided the password is strong and delivered separately. It cannot verify the recipient’s legal identity, secure an already compromised endpoint, or stop an authorized recipient from redistributing a downloaded file.
Nexynto Transfer states that transfer passwords are hashed on the server. Users should still avoid reusing account passwords and should not place the transfer password in the same email or chat message as the link.
Interpret download limits correctly
A download allowance governs requests accepted by the transfer service. It can help constrain repeated access and identify the intended delivery pattern. Network retries, browser behavior, and a recipient’s need to use more than one device should be considered when selecting a limit.
Once a recipient has downloaded a file, service-side controls cannot govern every subsequent copy. Use document-level protection, contractual controls, or a managed collaboration system when downstream use must be controlled more strictly.
Frequently asked questions
Does expiry delete a file from the recipient’s device?
No. Expiry stops future service access; it cannot remove copies downloaded before the link expired.
Does a one-download limit prevent copying?
No. It limits service-authorized downloads, not copies made after an allowed download.